
Tài nguyên / Industry Perspectives
Tài nguyên / Industry Perspectives
IT outsourcing (ITO) has become an increasingly common choice for organizations seeking access to specialized expertise while allowing their internal teams to focus on core business priorities.
In this model, an ITO provider often operates as an extension of the client’s IT capabilities. Depending on the scope of engagement, the provider may be granted access to business systems and privileged accounts, or may work directly with customer data as part of service delivery.
The deeper this involvement becomes, the greater the cybersecurity responsibility.
The 2026 Verizon Data Breach Investigations Report (DBIR) found that third-party involvement was present in 48% of the breaches analyzed, up from 30% the previous year. This reflects organizations’ growing reliance on technology vendors and other partners across their operational ecosystems.
For ITO providers, protecting data and managing access are therefore no longer purely technical requirements. They can directly influence customer trust, brand reputation and competitive capability.
When Third-Party Providers Become Part of the Data Protection Chain
Recent incidents demonstrate that data risks do not necessarily originate within systems managed directly by an organization. They can also emerge through technology partners and other third parties involved in service delivery.
In April 2025, Toppan Next Tech, a provider of printing and document-processing services to DBS Bank and Bank of China Singapore, experienced a ransomware incident. Attackers extracted data stored on Toppan’s systems. DBS reported that documents relating to approximately 8,200 customers could have been affected.
Notably, DBS’s own systems were not directly compromised. Even so, the bank suspended certain activities involving the vendor, increased account monitoring and proactively contacted affected customers.
The incident illustrates an important point: when a service provider becomes deeply integrated into a client’s operations, the scope of what needs to be protected extends beyond the provider’s own internal systems.
For ITO providers, cybersecurity requirements can vary significantly from one client to another, depending on the systems and data involved, compliance requirements, and the level of response expected when an incident occurs.
Maintaining all of the specialist capabilities required for every possible scenario can be challenging for an internal IT team, particularly when continuous monitoring or advanced investigation is required.
Rather than building every capability in-house, ITO providers can retain their core internal functions while working with a cybersecurity partner that brings the necessary expertise and relevant implementation experience.
This approach allows organizations to add specialist capacity when needed while continuing to focus internal resources on their core business and the quality of services delivered to customers.
NetGuardX Extends 24/7 Cybersecurity Monitoring Capabilities
NetGuardX provides cybersecurity monitoring through a 24/7 operating model, supporting activities from continuous monitoring and alert detection to analysis, incident response and in-depth investigation.
The service also maintains threat intelligence activities, reporting and ongoing system optimization through a tiered operating model:
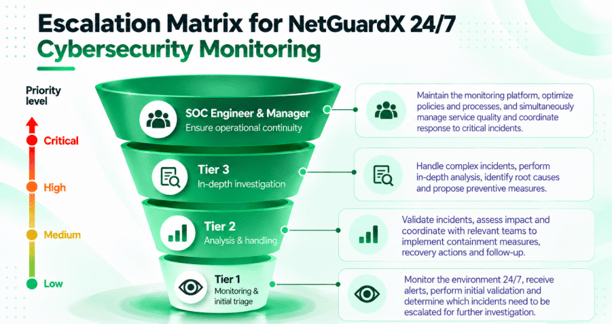
Alongside this tiered model, incidents are classified into four priority levels: Low, Medium, High and Critical.
Each priority level is associated with defined commitments for MTTD (Mean Time to Detect) and MTTR (Mean Time to Resolve), providing measurable operational benchmarks for monitoring service performance.
For ITO providers, this collaborative model makes it possible to retain control over customer relationships and systems while gaining access to 24/7 monitoring and specialist cybersecurity expertise when required.
It can also help reduce pressure on internal teams, narrow the gap between alert detection and response, and support more consistent service delivery in the face of cybersecurity risks.
Hotline: 1900 1586
Email: marketing@netnam.vn
Website: https://netnam.com/netguardx
NETNAM CORPORATION – 30 years of trusted internet & managed IT solutions and services for businesses
Headquater: 2nd Floor, HITC Building, 239 Xuan Thuy Street, Cau Giay Ward, Hanoi
Ho Chi Minh City Branch: 7 Nguyen Thi Minh Khai Street, Sai Gon Ward, Ho Chi Minh
Representative Office: 2 Quang Trung Street, Hai Chau Ward, Da Nang
Reference:
Doanh nghiệp của bạn mất bao lâu để phát hiện một cuộc tấn công? NetGuardX đánh giá hiện trạng và bàn giao đề xuất lộ trình giám sát trong 5 ngày làm việc.
Đặt lịch đánh giá